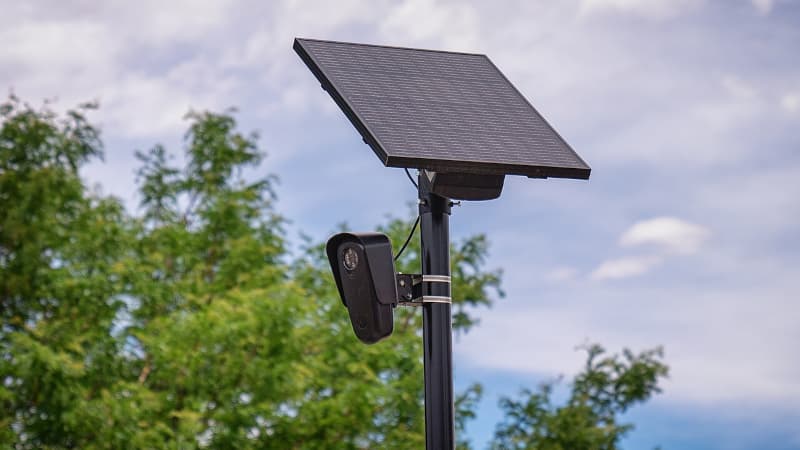
Flock Safety surveillance cameras, deployed by law enforcement agencies across the United States, are running Android 8.1, a version released in 2017 and long out of active security support. Researcher Micah Lee dumped the disk contents of one of these units and found unpatched known vulnerabilities baked into the OS. Android 8.1 is the version current when Flock Safety was founded, possibly by coincidence, possibly not.
The more damaging finding is a hard-coded API key embedded in the firmware. Any attacker with a camera's MAC address can query Flock's backend infrastructure using that key, pulling data from any camera on the network. This is not a sophisticated exploit. It is a credential left in plain sight on a device marketed specifically to police departments.
Lee's full writeup details the specific API behavior, the scope of accessible data, and the remediation problem Flock now faces: revoking a network-wide key without a per-device update mechanism could take down the entire fleet. Read it for the technical depth on how the key was found and what it actually exposes. The story is not over and more researchers are looking.
[READ ORIGINAL →]