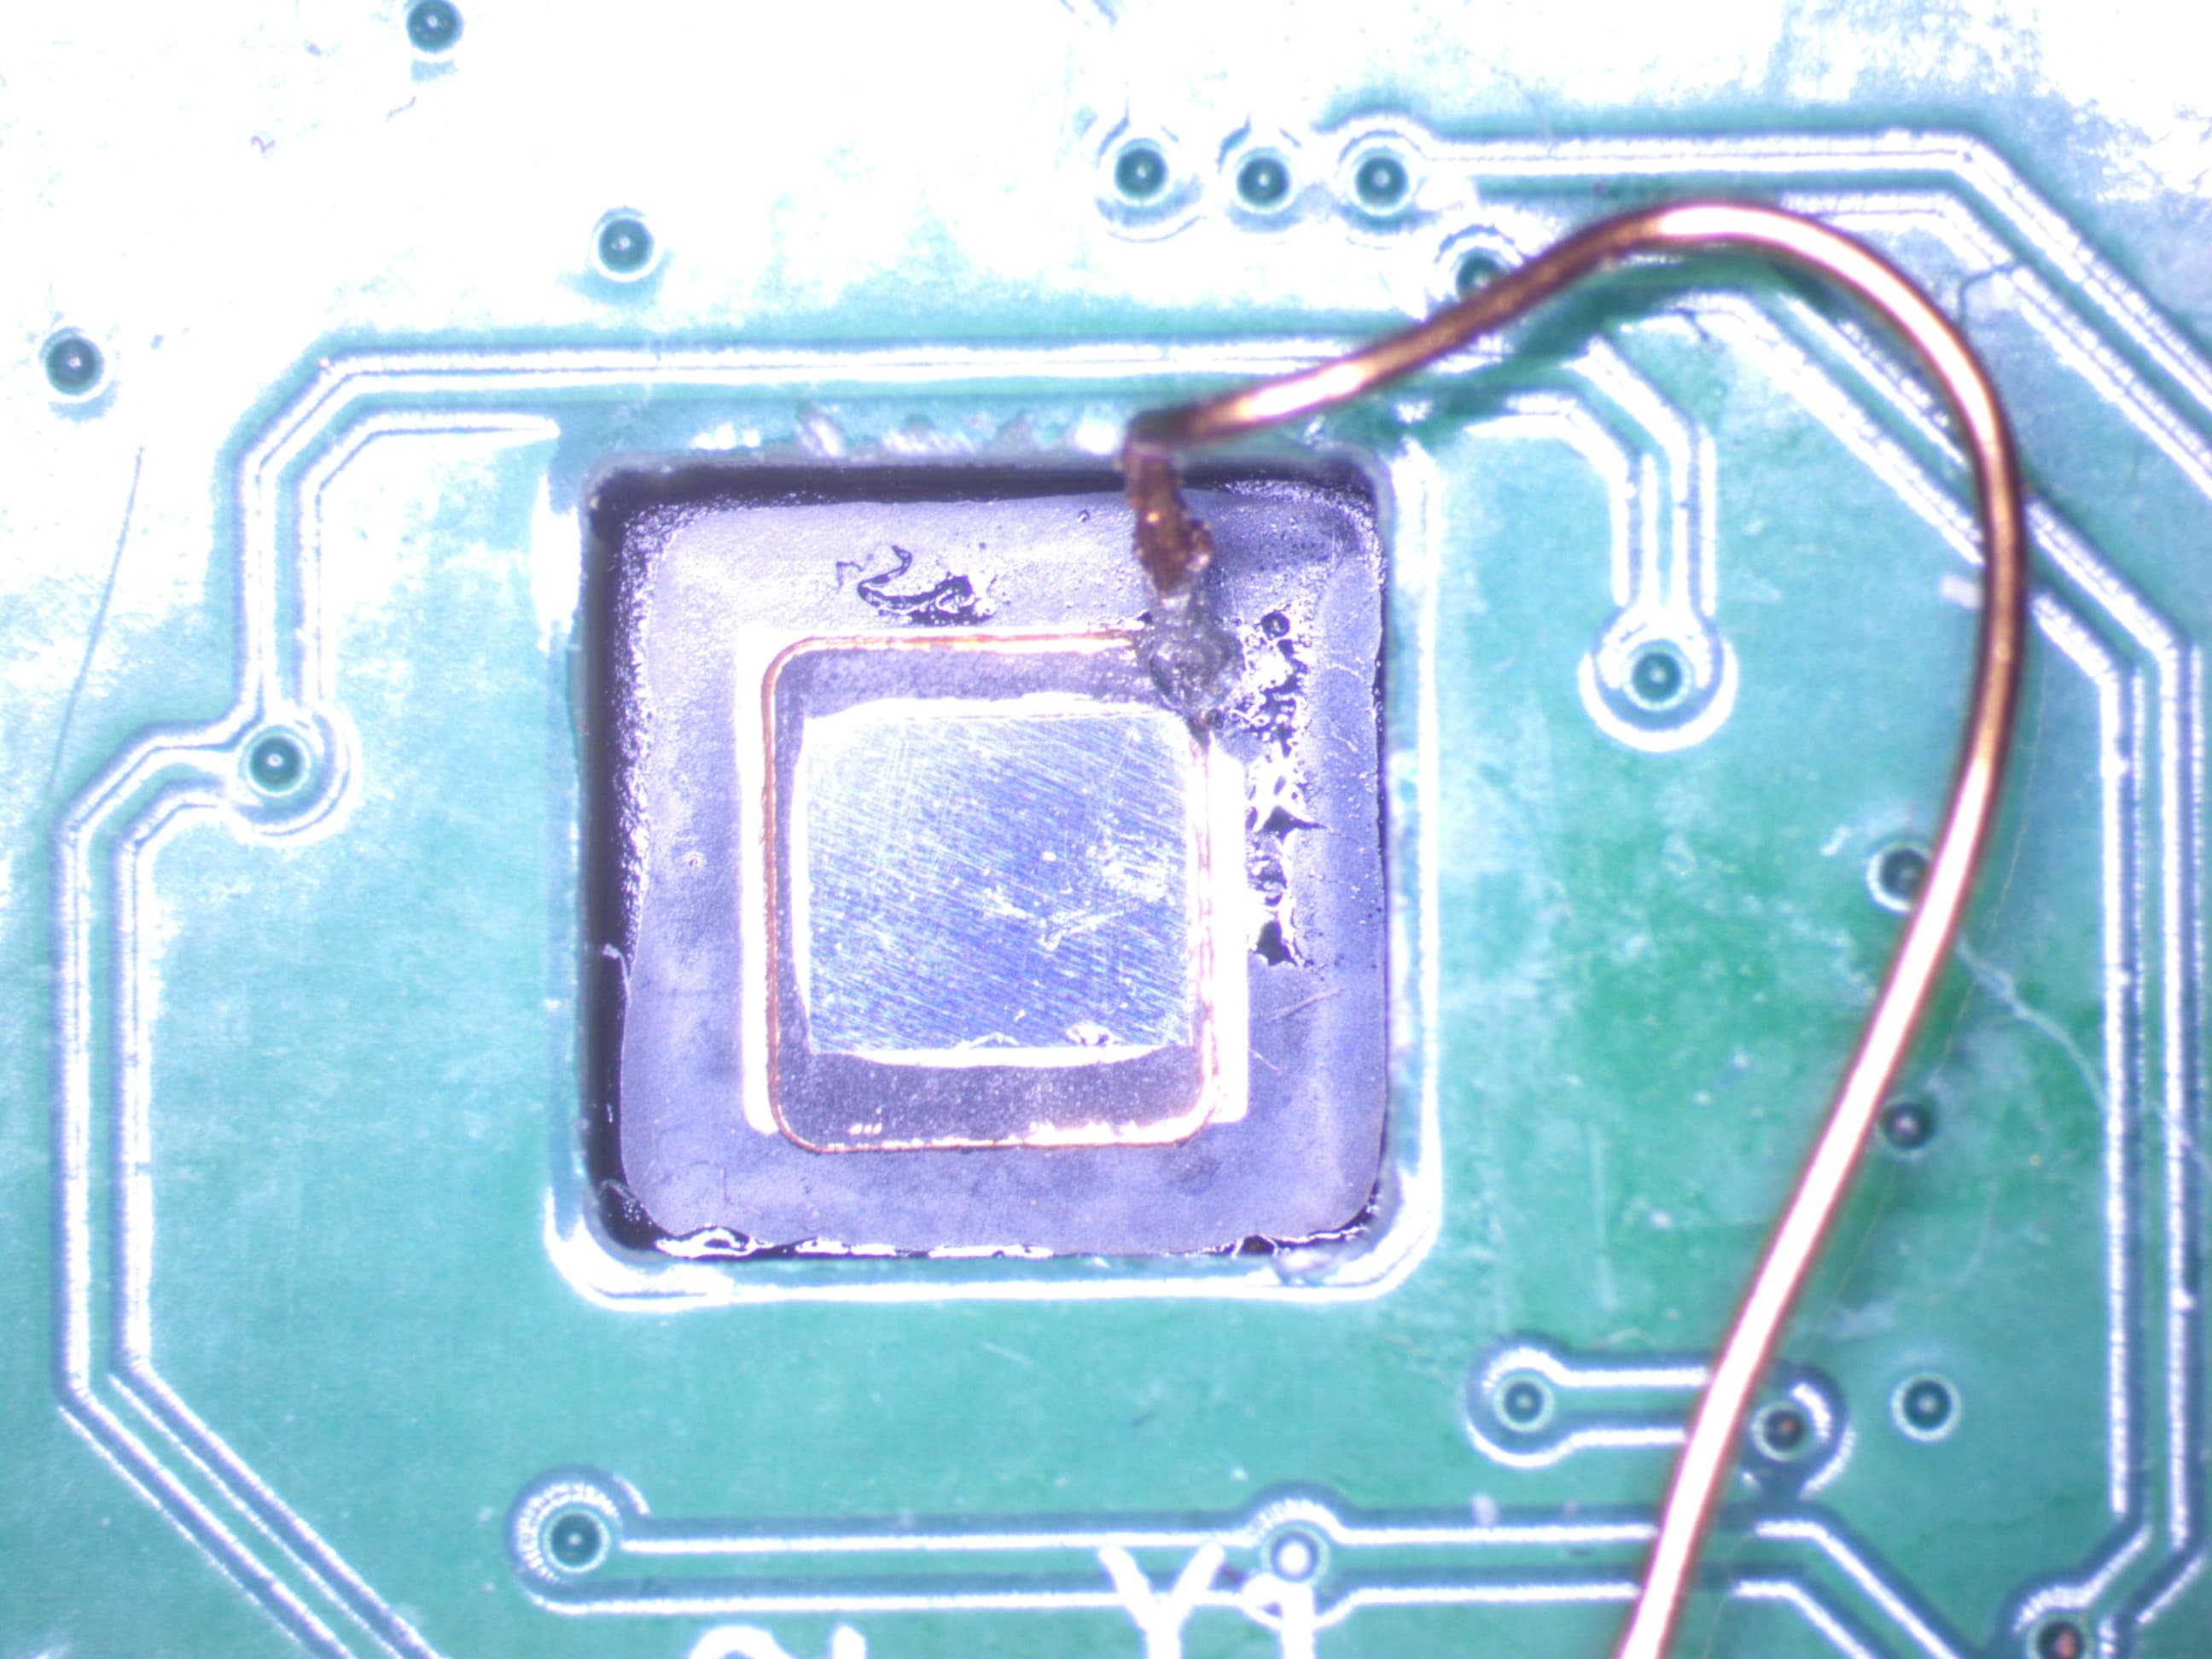
Ledger Donjon cracked the RP2350's secure debug lockout using laser fault injection, then read the 128-bit secret Raspberry Pi hid in memory as part of the official RP2350 hacking challenge. The RP2350 is not a soft target: it runs ARMv8 TrustZone, supports permanent debug disable via OTP fuses, and includes active glitch detection that blocks the voltage-zap attacks that work on lesser chips.
The attack cost $250,000 in lab equipment and required decapsulating the chip from the backside, then using photon-emission electron microscopy to locate the debug-enable register on the die. The laser was fired through the silicon wafer using IR, flipping bits in the register without destroying the chip. After a reset, the secure execution zone was fully accessible.
Read the original Ledger Donjon writeup for the methodology behind the die mapping, the specific shot placement logic, and what this means for secure boot assumptions on embedded hardware. The finding does not make the RP2350 useless for security applications, but it sets a concrete cost and capability floor for physical attacks against it.
[READ ORIGINAL →]